Quickly audit-ready
Prepare SoA, internal audits & management reviews in a structured manner - including evidence & exports.
Are you looking for an ISMS tool that will help you implement ISO 27001 & NIS2 faster and in an audit-ready manner?
Non-binding, online, approx. 45 minutes




In six points: Why companies choose HITGuard as their ISMS tool.
Prepare SoA, internal audits & management reviews in a structured manner - including evidence & exports.
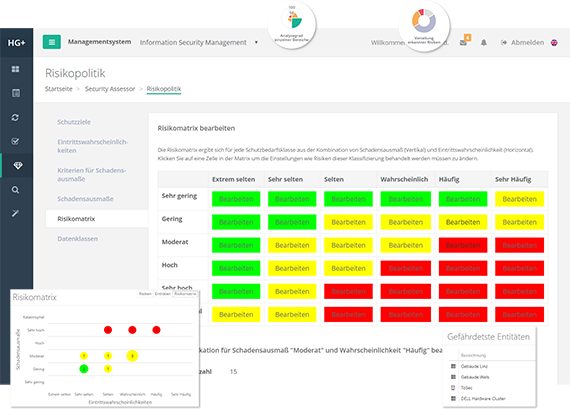
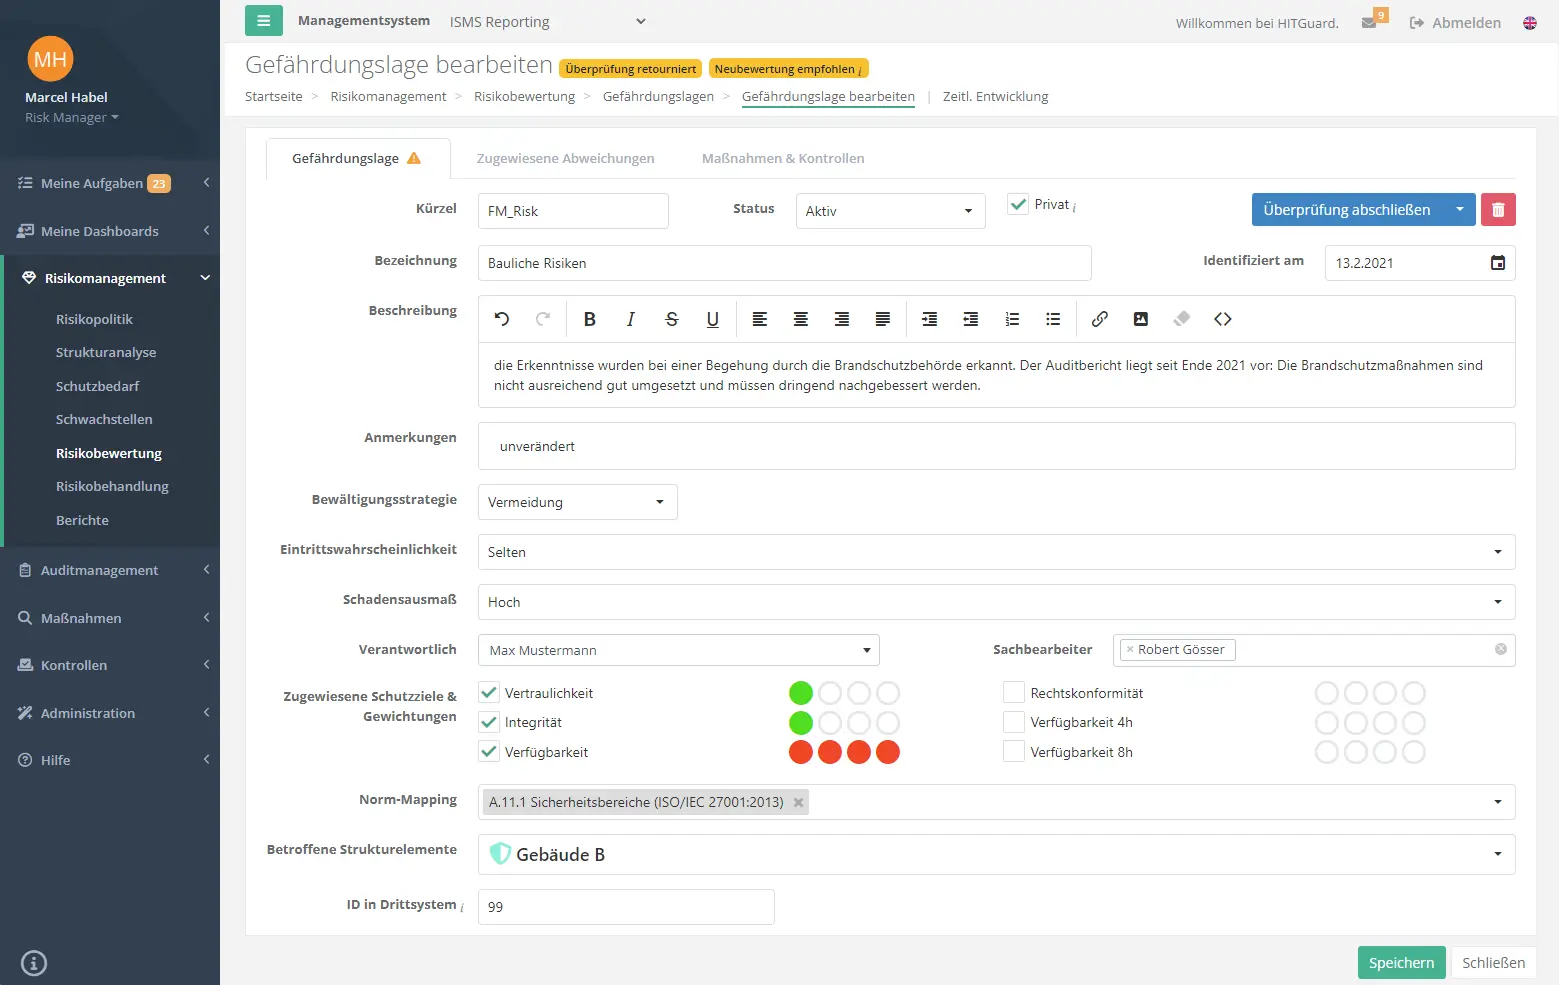
Risk management according to ISO 31000 with workflows, evaluations and historization.
Checklists and knowledge databases for guidelines, processes and controls - ready to go.
Flexible operation - in your infrastructure or as SaaS with hosting in Germany.
Clients, roles and collaboration across teams and locations.
Intelligent answer suggestions, translations, risk/measure/control suggestions, answers to related questions
Everything you need for efficient information security management - centralized, traceable and audit-ready.
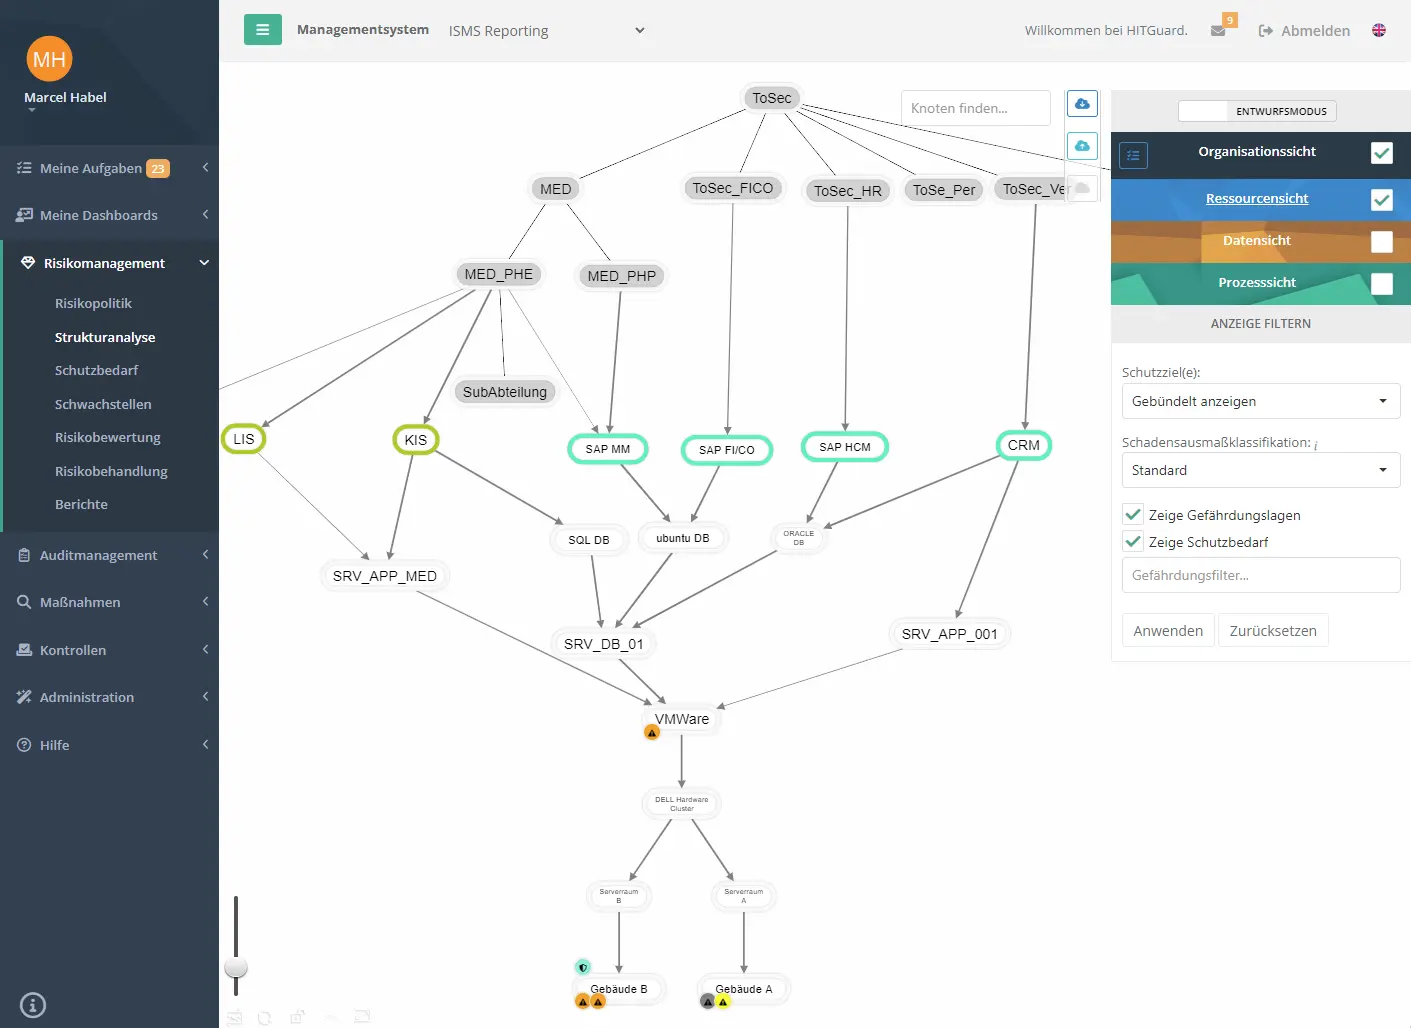
Identification, assessment, treatments, accepted risks & progress documentation - with workflows and history.
Explanation of applicability, controls, tasks, deadlines & evidence - all audit-proof and traceable.
Internal audits, findings, action tracking, re-tests and management reviews prepared and documented.
Templates & libraries for guidelines, process and control descriptions - versioned and multilingual.
Maturity level, risks, measures, audit plan & compliance status at a glance - including exports.
Flexible operation in own infrastructure or as EU SaaS, role/rights model, clients & integrations.
From the initial gap analysis to the monitoring audit: structured evidence, clear responsibilities and clean exports.
Audit program, checklists, deviations, measures & proof of effectiveness - incl. re-test.
Combine input/output in a structured manner: Key figures, risks, audit results, improvements, resources.
Consistently store, version and export evidence for auditors - without tool breaks.
Regulatory requirements under control - with content, mappings and reports for D-A-CH.
Set requirements from NIS-2 / IT-Grundschutz against existing controls - prioritize & close gaps.
Structured controls, action plans, responsible persons, due dates & effectiveness checks.
Assessments, risk scores, measures & re-assessments - transparent across the entire supply chain.
Neutral overview of selected criteria.
| Criterion | HITGuard Recommended | verinice | HiScout ISM | ISMS.online |
|---|---|---|---|---|
| Provision | Cloud (DE) & On-Prem | Server/Client, Open Source | On-prem/cloud depending on setup | Cloud SaaS |
| Focus ISO 27001 | SoA, internal audits, MR, exports | ISO 27001 & IT baseline protection | ISO 27001/2, Enterprise context | ISO 27001, preconfigured packages |
| IT baseline protection suitability | Practice in D-A-CH (mappings/reports) | IT baseline protection focus | Strong in the public sector | Primarily ISO 27001 |
| Templates & knowledge bases | Checklists, knowledge databases | Libraries/Models | Suite templates/modules | Policy Packs & Templates |
| Operating model & scaling | Clients, roles/rights, integrations | Depending on edition/setup | Wide range of enterprise options | Clients in SaaS plan |
| Open Source | - | Yes (GPLv3) | - | - |
| Typical target groups | Medium-sized companies → Enterprise | Broad spectrum incl. OS affinity | Large organizations/authorities | Companies with a cloud focus |
The most frequently asked questions about ISMS tools, ISO 27001 software and NIS-2 - answered briefly and clearly.
Both mean software for introducing and operating an information security management system. Modern solutions bundle risk management, SoA/controls, audits, templates and evidence centrally - often with a cloud option.
Through structured SoA maintenance, audit planning with findings and re-tests, management review preparation and clean evidence & exports. Responsibilities, due dates and reminders ensure that nothing is left undone.
Yes, HITGuard covers the core processes of the ISMS and supports work with NIS-2 and IT-Grundschutz by means of mappings, reports and exportable evidence. evidence for working with NIS-2 and IT-Grundschutz.
Yes, HITGuard can be operated in your own infrastructure or used as an EU SaaS. Roles/rights, client capability and integrations (e.g. IdP, DMS, ticketing) are configured on a project-specific basis.
This depends on the starting level and scope. With templates, workflows and centralized evidence, early audits can often be prepared much faster to prepare. A guided demo clarifies requirements and timeline.
Licensing depends on the deployment scenario, user roles and optional modules. We will be happy to prepare a suitable offer including an implementation and operating concept.

"I have gained experience with several comparable tools in my professional career and recommend HITGuard to a wide range of users: those who struggle with a lack of resources in information security; those who are introducing a new ISMS or have to meet certain requirements as KRITIS operators; and those who want to switch from one tool to a new one and want quick results."

Chief Information Security Officer


"As Head of Governance, Risk, and Compliance, I have been using HITGuard since 2023 to continuously process my recorded risks and controls, which I have assigned to various business areas for implementation. HITGuard has proven to be an extremely intuitive and affordable GRC tool."

Head of Governance, Risk & Compliance Management
Treffen Sie uns im Herbst auf der it-sa in Nürnberg! Sie finden uns in Halle 7, Stand 200. Wir freuen uns auf Ihren Besuch!